KNOWLEDGE ARTICLE
What Is X-Frame-Options?
Frame embedding restrictions, clickjacking protection
Restricts whether other pages can embed a response in frames or iframes.
At a glance
DENY prohibits embedding; SAMEORIGIN permits same-origin framing. CSP frame-ancestors can express more detailed allowed-origin rules.
Reducing opportunities for clickjacking
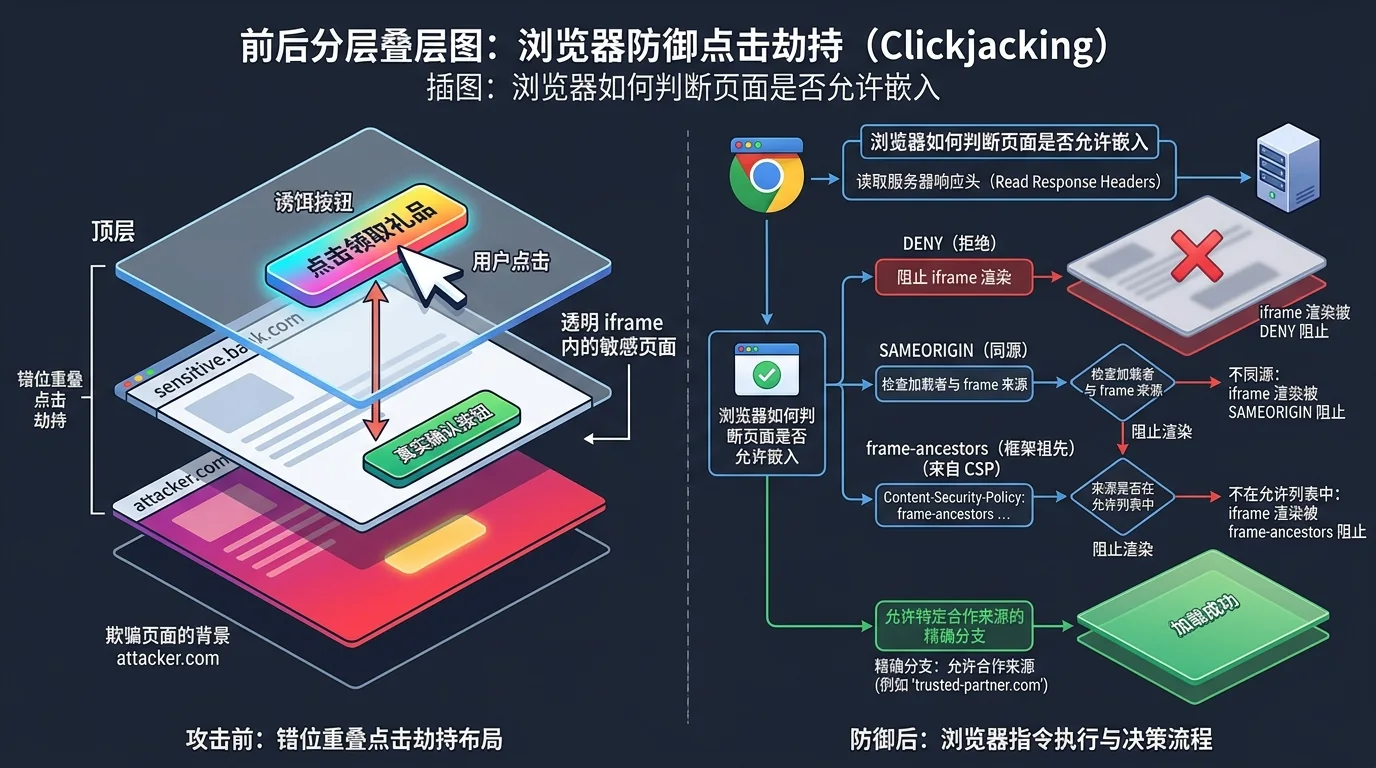
An attacker may transparently embed or misalign a target page so that a user appears to click a decoy while operating the real site. This is clickjacking. X-Frame-Options limits embedding through DENY or SAMEORIGIN, reducing opportunities to overlay sensitive interfaces.
DENY disallows all framing; SAMEORIGIN allows same-origin pages. Historical ALLOW-FROM support is inconsistent and unsuitable for modern deployment. CSP frame-ancestors permits multiple allowed origins and more granular rules.
How browsers decide whether to render a frame
- After receiving an iframe response, the browser evaluates X-Frame-Options and CSP frame-ancestors against the ancestor origins before rendering.
- Same-origin checks concern the ancestor chain and browser behavior. Do not infer complex nested-frame outcomes from only the outer URL.
- Conflicting X-Frame-Options values can produce inconsistent client behavior. Generate a coherent policy at one response layer.
- A header protects the response carrying it. A protected homepage does not cover omitted policies on login, payment or settings pages.
Designing legitimate partner embedding
Payments, reports and white-label portals may require cross-site framing. Allow precise partner origins through frame-ancestors and separate sensitive operations from embeddable presentation pages. Avoid opening the entire site to solve one integration need.
SameSite cookies, reauthentication, explicit confirmations and careful interface design can complement framing controls. JavaScript frame-busting is easier to bypass and should not replace browser-enforced response policies.
Practical use and interpretation
DENY, SAMEORIGIN and frame-ancestors provide evidence of the current page's framing restrictions. When both mechanisms are present, check consistency rather than scoring the number of headers.
Missing X-Frame-Options does not imply missing protection: CSP may provide equivalent or stronger controls. Confirmed absence of both supports a narrow statement that no response-level framing restriction was observed. Exploitability still depends on page operations and other defenses.
Points to consider
CSP can supply equivalent protection when this header is absent, so inspect both mechanisms.
Frequently asked questions
Should frame-ancestors and X-Frame-Options both be set?
Modern browsers support frame-ancestors. X-Frame-Options can help older clients, but their policies should remain consistent.
Does SAMEORIGIN allow every subdomain?
No. Same origin requires matching scheme, hostname and port. Different subdomains are not automatically same-origin.
Does absence of both headers prove clickjacking?
No. Framing behavior, sensitive actions and other protections matter. Their absence removes one defensive layer, not every possible safeguard.