KNOWLEDGE ARTICLE
What Is HTTP Response Headers?
HTTP Headers
Response fields describing content, caching, redirects and security policies.
At a glance
Headers are not displayed as page content, but tell browsers how to interpret, cache and protect it. They may also disclose server or framework information.
What are HTTP response headers?
An HTTP response normally contains status information, headers and a body. Headers describe MIME types, caching, redirects, security policies, cross-origin access and server behavior. Although they are not shown like page text, they affect how browsers and search engines process resources.
The same page can return different headers for different methods, regions, devices, login states or CDN nodes. An observed response is a verifiable snapshot, not an immutable configuration.
Common categories of response headers
- Content-Type declares the MIME type. Content-Length and Date describe properties of the response.
- Cache-Control, ETag, Last-Modified and Vary jointly govern HTTP caching and revalidation.
- HSTS, CSP, X-Frame-Options, X-Content-Type-Options, Referrer-Policy and Permissions-Policy give browsers protective instructions.
- Location and status codes describe redirects; Access-Control-Allow-Origin participates in CORS; X-Robots-Tag can influence search-engine processing.
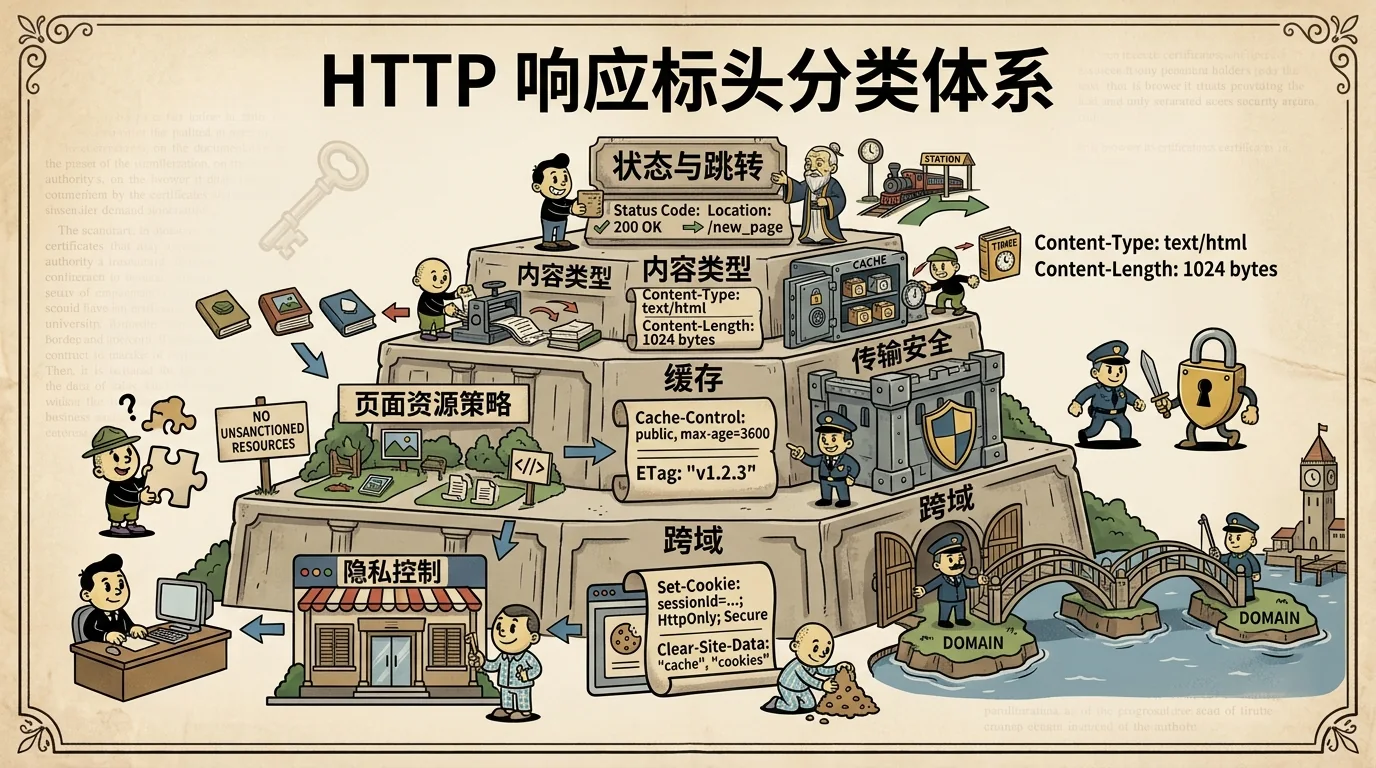
Possible effects on security, performance and SEO
- Persistent 200, 301, 404 or 503 responses lead search engines to handle URLs differently. A single 5xx response needs context about duration and recurrence.
- Good caching can reduce transfer volume and server load. Actual speed also depends on resource type, cache-hit rate, CDN behavior and real-user measurements.
- A complete set of security headers suggests basic hardening. A missing header means a particular protection is absent, not that the corresponding vulnerability necessarily exists.
- Server, X-Powered-By and debug headers may reveal technology clues. A specific vulnerability claim needs a confirmed version and an applicable advisory.
Practical use and interpretation
Headers combined with TLS, page behavior and public technology signals give a fuller configuration profile. A software name and an exact version have different evidential strength. Specific risk claims are appropriate only when an identified version corresponds to an applicable public security record.
If evidence about a CDN, WAF, CORS policy or authentication method is insufficient, its status is unknown. Firm conclusions require an explicit response; inferred consequences should be expressed conditionally.
Points to consider
Appropriate headers improve caching and help reduce browser-side risks such as clickjacking and content sniffing.
Frequently asked questions
Does a missing security header mean a vulnerability exists?
No. It means one defense-in-depth signal is absent. Exploitability depends on application code, input and output handling, and the actual attack surface.
Why do headers change between visits?
CDN nodes, cache hits, A/B tests, region, login state and server updates can all change the response.
Do more headers mean a more professional setup?
Not necessarily. Headers should have clear caching, security or content semantics. Redundant, conflicting or debug information can create problems.