KNOWLEDGE ARTICLE
What Is DMARC?
Domain-based Message Authentication, Reporting and Conformance
Defines handling and reporting policies for messages that fail aligned email authentication.
At a glance
DMARC can request monitoring, quarantine or rejection of failing messages, while reports help domain owners identify legitimate senders and impersonation.
Connecting the visible sender to authentication results
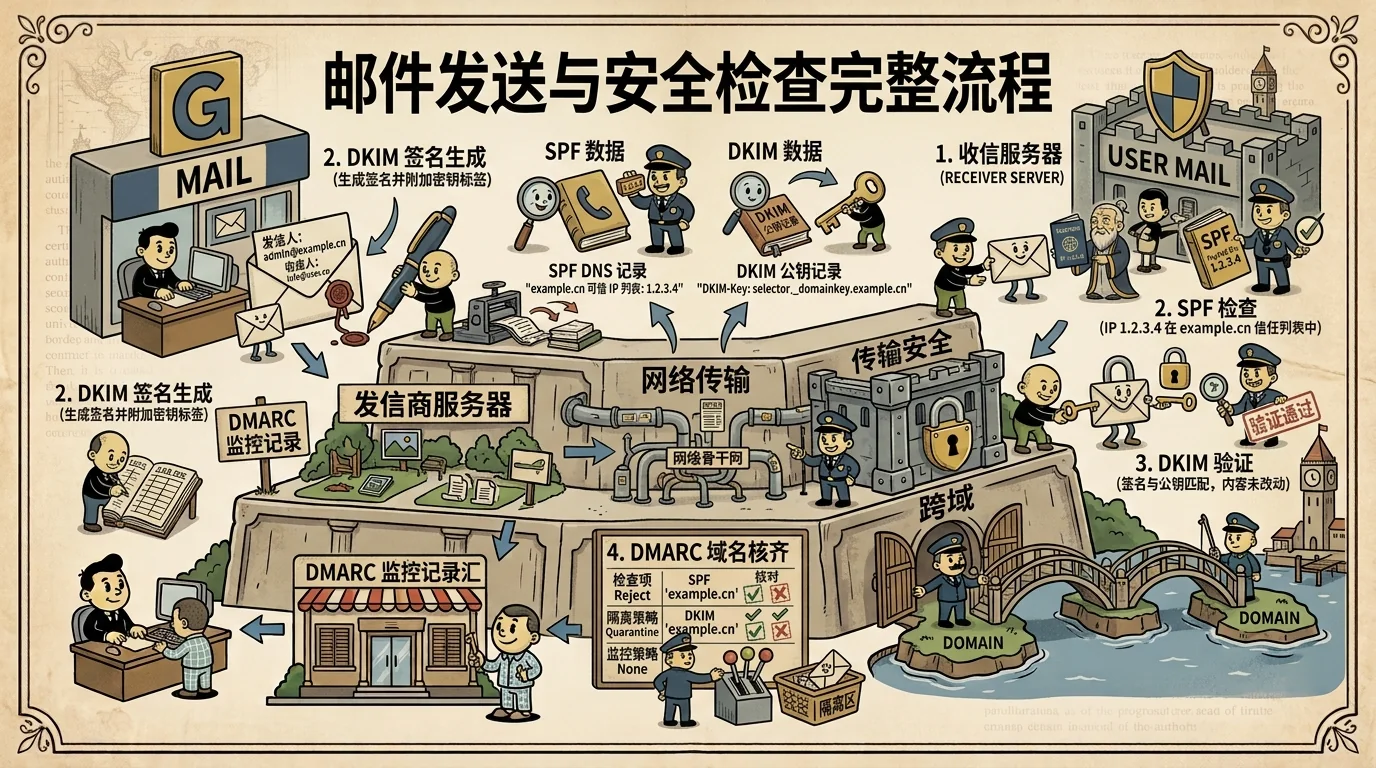
DMARC focuses on the domain users see in the From address. At least one passing SPF identity or DKIM signing domain must align with that domain. This prevents an attacker from passing SPF or DKIM for an unrelated legitimate domain while impersonating a brand in the visible From field.
The domain publishes a policy at its _dmarc name. Recipients use p=none, quarantine or reject to guide handling of messages that fail alignment and may send reports to rua or ruf addresses. DMARC is not a new encryption algorithm: it combines existing authentication, identity alignment and handling policy.
Moving from monitoring to rejection
- p=none commonly collects aggregate reports to establish the real sending inventory; it does not request mandatory quarantine of failing messages.
- During migration, pct can apply policy to a proportion of non-compliant traffic. Staying at a low percentage leaves the rest without that requested enforcement.
- aspf and adkim select relaxed or strict alignment. Relaxed alignment permits a shared organizational domain; strict alignment requires an exact domain match.
- Subdomains may inherit a parent policy, with sp specifying a separate subdomain policy. Large organizations should check inactive subdomains and legitimate third-party sending needs.
Using reports to manage sending services
Aggregate reports group messages by source IP, authentication and alignment outcomes. They help identify unknown platforms, configuration gaps and possible impersonation. Volumes can be large, so specialized parsing is common. The reports describe recipients' observations, not complete message content.
Before tightening policy, check business systems, SaaS services, forwarding and mailing lists. Moving directly from no policy to reject can disrupt legitimate mail. Gradual enforcement after a representative reporting period makes exceptions easier to diagnose while preserving delivery.
Practical use and interpretation
The published policy, percentage, alignment modes and presence of reporting addresses can be displayed directly. p=reject normally expresses stronger enforcement intent, but protection depends on correct SPF or DKIM, alignment of legitimate senders and recipient enforcement.
When no _dmarc record is returned, first exclude DNS errors. If a domain is known to send mail but lacks a policy, impersonation protection may be weaker. If its mail usage is uncertain, the appropriate status is unknown.
Points to consider
A strict, correctly deployed DMARC policy can substantially reduce impersonation of a brand's sending domain.
Frequently asked questions
Is p=none the same as having no DMARC?
No. Authentication and reporting can still operate; the policy simply does not request quarantine or rejection. It is commonly used for monitoring.
Must both SPF and DKIM pass DMARC?
No. DMARC can pass when either SPF or DKIM passes and its authenticated domain aligns with the visible From domain.
Why can impersonation still occur with reject enabled?
Recipients may not enforce the policy, attackers may use lookalike domains or misleading display names, or subdomain coverage may differ. Inspect the complete headers to distinguish these cases.