KNOWLEDGE ARTICLE
What Is CDN?
Content Delivery Network
Delivers content from edge nodes nearer users and reduces origin load.
At a glance
A CDN can cache static or eligible dynamic content, conceal some origin details and provide traffic filtering or web protection.
Delivering content closer to users
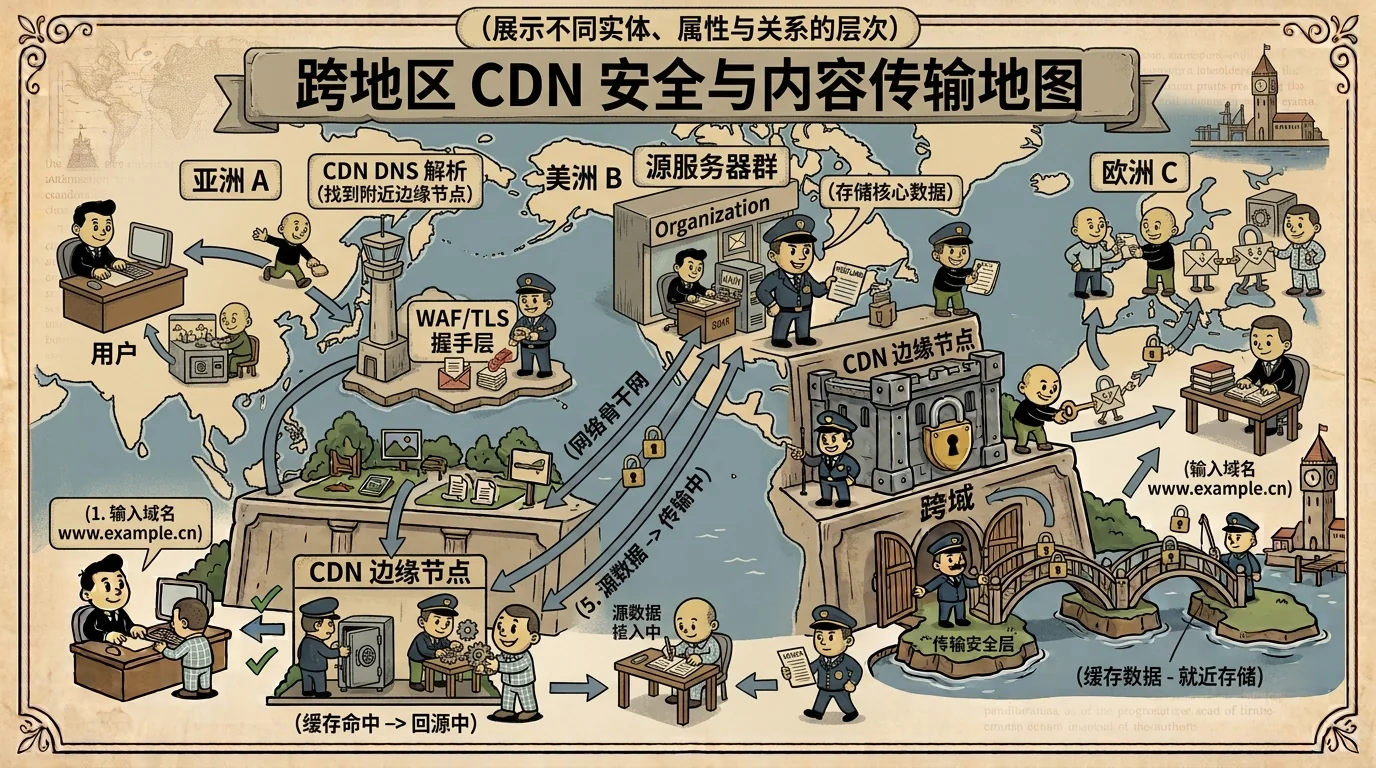
A CDN deploys edge nodes in multiple regions and uses DNS, Anycast or platform routing to direct users to a suitable entry point. Cached static and eligible dynamic responses can be returned without an origin request, reducing long-distance transfers, origin load and traffic spikes.
Modern CDNs do more than cache images. They may terminate TLS, compress content, optimize protocols, apply WAF and bot policies, balance load and provide failover. Available features depend on plan and configuration; a provider name does not prove every feature is enabled.
Cache hits and origin requests
- DNS directs the user to an edge address, where TLS terminates. The edge looks up a cache object using the host, path, query parameters, cookies and configured key.
- A cache hit returns directly. A miss or stale entry may trigger an origin request, with storage determined by Cache-Control, platform rules and response status.
- Objects can be revalidated after TTL expiry or purged by a publishing workflow. Global invalidation takes time to propagate.
- Dynamic requests may pass through, run edge code or use layered caching. Headers sometimes expose HIT, MISS, Age and node identifiers.
Why cache keys and origin protection matter
Incorrectly ignoring cookies, Authorization or language parameters can expose personalized responses to other users. Including every query parameter can fragment the cache. Design policies around whether content is public or personalized and how it changes; handle logged-in pages cautiously.
Protecting an origin requires limiting inbound access to the CDN, authenticating origin requests and considering historical DNS exposure. A directly accessible origin can bypass edge WAF and rate limits. CDN capacity and filtering do not replace application fixes or origin security.
Practical use and interpretation
CNAME, ASN, issuer and header evidence together can identify a CDN more confidently. An edge IP's city describes a network node, not necessarily the company or origin location.
No familiar CDN markers does not establish direct origin exposure: white-label services, private proxies or unrecognized providers may be involved. Cache behavior is resource-specific; one homepage MISS does not mean the entire site is uncached.
Points to consider
A CDN often helps speed and availability, but results depend on cache policy and origin configuration.
Frequently asked questions
Does a CDN always make a website faster?
It can reduce distance and origin load, but poor cache policy, coverage, origin connectivity or page design can limit the benefit.
Is a CDN IP the real server address?
Usually it is an edge entry point. The origin may be elsewhere, and concealment depends on DNS history and firewall configuration.
Can a CDN replace security fixes?
No. WAF and traffic filtering reduce some pressure, but application vulnerabilities, account permissions and origin configuration still need direct remediation.