KNOWLEDGE ARTICLE
What Is WAF?
Web Application Firewall
Detects and blocks some malicious HTTP traffic before it reaches an application.
At a glance
Often deployed with a CDN or reverse proxy, a WAF filters requests using rules, reputation and behavioral signals.
What a WAF inspects
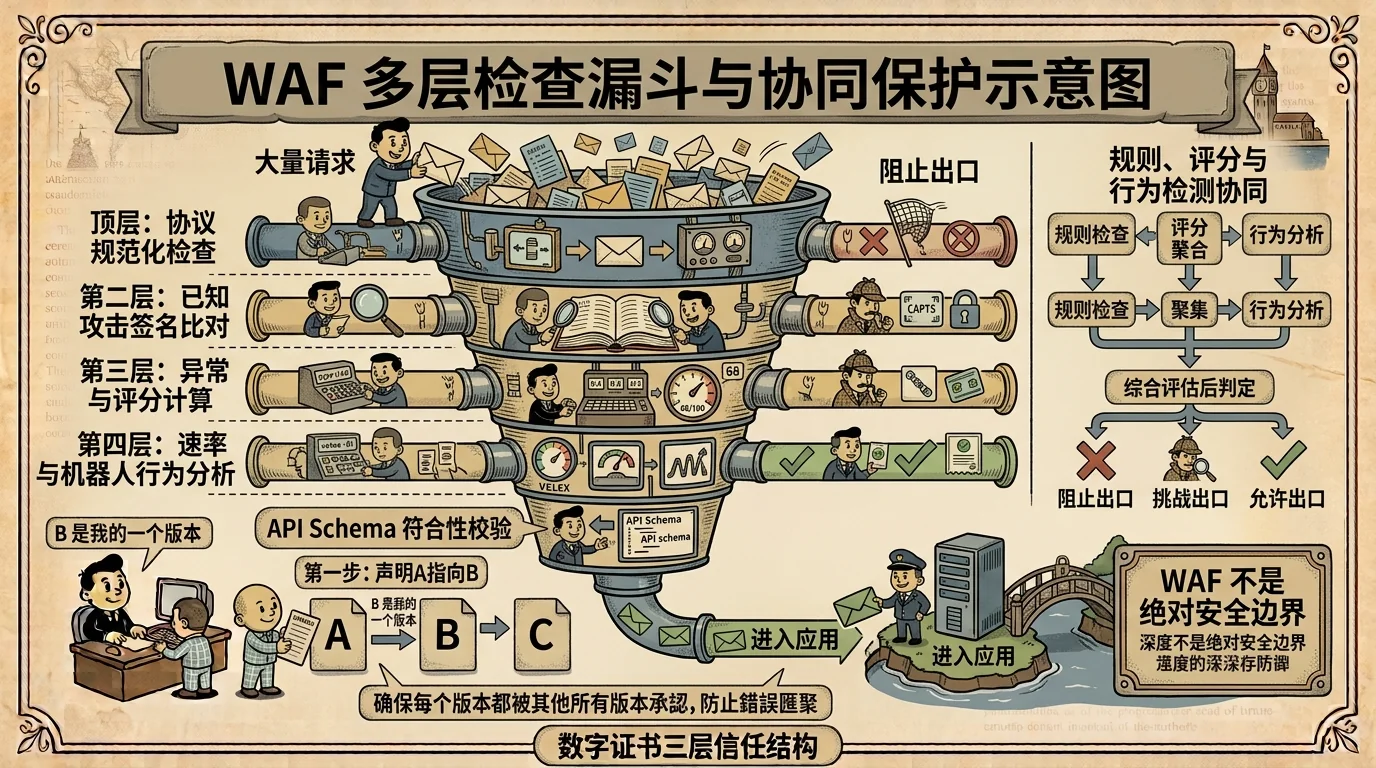
A Web Application Firewall sits between clients and a web application. It inspects HTTP/HTTPS requests and sometimes responses for SQL injection, XSS probes, path traversal, malicious bots and other patterns using rules, reputation, behavior and rate. Deployment points include CDN edges, cloud load balancers, reverse proxies and hosts.
A WAF sees protocol and application traffic but does not inherently understand every business rule. Broad rules miss variants; strict ones can block legitimate users. Encrypted traffic needs TLS termination where inspection is possible. A WAF reduces common attacks and can buy remediation time, not replace secure development.
Combining rules, scores and behavior
- Signatures recognize known attack syntax. Anomaly scoring combines weaker signals before blocking, avoiding excessive reliance on one sensitive rule.
- A positive model allows requests matching API schemas, parameter types and business limits. It can be precise but requires ongoing maintenance.
- IP reputation, device signals, rate limits and challenges help address scans and automated traffic. Legitimate high-volume APIs need an appropriate baseline.
- Detection mode records events; blocking mode denies requests. Log replay, gradual rollout and exception management help reduce false positives.
Why direct origin access weakens coverage
If an attacker can find and connect directly to the origin, traffic may bypass the edge WAF. Restrict origin access to trusted proxies, authenticate origin connections with certificates or signatures, and consider exposure through historical DNS, mail headers and error pages.
Protecting the main hostname alone leaves possible gaps at APIs, upload hosts, old subdomains and alternate ports. Coverage depends on an asset inventory and consistent traffic entry points; one homepage marker cannot prove all services are protected.
Practical use and interpretation
Challenge pages, characteristic cookies, headers and network ownership can indicate a WAF, but providers may hide or customize them. Explicit platform evidence or observed filtering supports a firmer identification.
A detected WAF suggests an additional traffic-protection layer, not a vulnerability-free application. Absent markers leave the state unknown rather than proving no protection or an exposed origin.
Points to consider
A WAF reduces common attack pressure but cannot replace fixes to application vulnerabilities.
Frequently asked questions
Do I still need to fix vulnerabilities behind a WAF?
Yes. Rules can be bypassed and cannot model every business operation. Code, dependencies and permissions still need correction.
Why does a WAF block legitimate users?
Valid inputs may resemble attack patterns, or rate, region and device policies may trigger. Tune rules using logs and real business baselines.
Does no WAF header mean no WAF?
No. Providers can hide markers, use white-label configurations or protect selected paths. Insufficient evidence means unknown.