KNOWLEDGE ARTICLE
What Is X-Content-Type-Options?
MIME sniffing restrictions
Asks browsers to respect declared media types rather than reinterpret data as executable content.
At a glance
The usual value, nosniff, restricts MIME sniffing. It must accompany correct Content-Type declarations and cannot repair incorrect server metadata.
Why nosniff enforces declared types
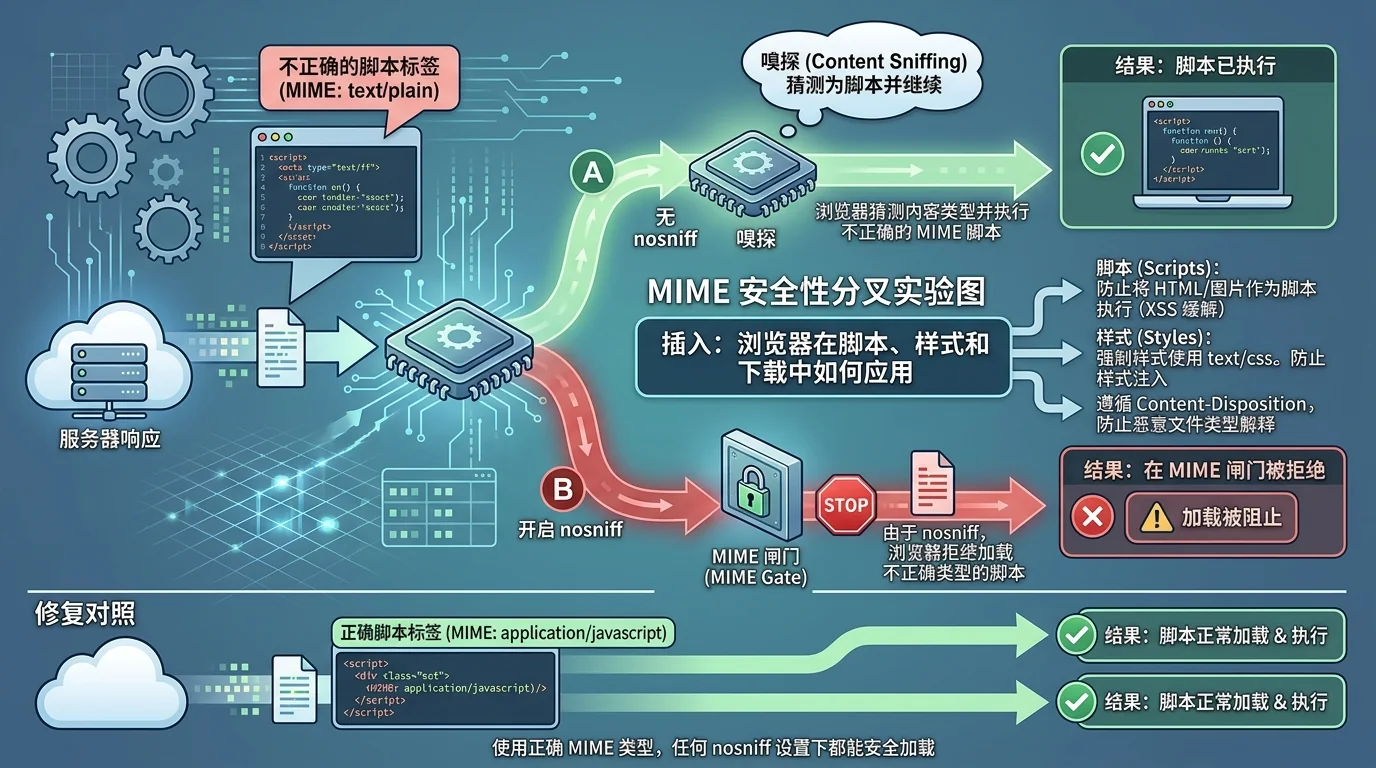
X-Content-Type-Options: nosniff instructs browsers not to infer a different MIME type in relevant resource contexts. Its key role is to stop ordinary data being reinterpreted as executable scripts or styles, tightening the boundary between a server declaration and browser behavior.
Nosniff is not a universal content validator and cannot correct Content-Type. If JavaScript has the wrong type, strict handling may block it and break functionality. Ensure static assets and APIs have correct media types before enabling the policy.
Scripts, styles and downloads
- Script and stylesheet requests receive strict MIME checks. Inappropriate types may prevent execution or application.
- Cross-origin reads are also governed by Fetch, CORS and CORB/ORB mechanisms. Nosniff is one signal within a broader content boundary.
- Uploaded files still need safe types, separate origins and suitable Content-Disposition even when nosniff is present.
- CDNs can cache incorrect Content-Type values. Correct the origin, purge affected caches and verify responses from different edges.
Checks before enabling nosniff
Sample JavaScript, CSS, JSON, fonts, WebAssembly and downloads. Repair routes relying on extension guesses or a server-wide text/plain default. Modern build systems often supply correct types, while older static servers and object-storage metadata are common gaps.
After deployment, inspect browser MIME-refusal errors. Ensure an error page does not return 200 and an unsuitable type from a script URL. Correct status codes and strict media handling work together for predictable clients.
Practical use and interpretation
An explicit nosniff value shows a request for stricter media-type handling. Correctness still depends on the actual Content-Type; a present header with wrong metadata can create availability problems.
Absence does not prove an existing sniffing vulnerability. Risk inference also needs conditions such as user-controlled responses, executable contexts and relevant browser behavior.
Points to consider
A missing header means this extra constraint was not observed; it does not establish an exploitable sniffing flaw.
Frequently asked questions
Why does a script stop loading after nosniff is enabled?
Its Content-Type may be wrong. The browser stops tolerant guessing; fix the server's media type.
Does nosniff prevent all upload risks?
No. Uploads still need validation, origin isolation, safe download handling, permissions and suitable sanitization.
Does nosniff eliminate XSS?
No. It limits particular MIME-sniffing paths. HTML injection, unsafe DOM operations and other execution paths can still cause XSS.