
 murf.ai
 Paid content
Categories: Artificial Intelligence
Generate human-like speech and deploy Conversational agents with Murf AI. The complete AI Voice platform trusted by 10 million+ developers, businesses, and creators.
 Visit website
 Updated: 2026-09-21 13:03
 Language: English (default)
 Access: Normal
 Profile views 1
 Outbound visits 0
Related questions
More questions →What Can You Actually Do With a Free Hosted REST API Like ReqRes?
A free hosted REST API like ReqRes gives you a real HTTP endpoint you can call immediately—no signup, no local server, no database setup. You get predictable JSON responses for users, resources, login, and registration, which makes it useful for front-end demos, integration tests, learning HTTP clients, and prototyping. What it is not is a production backend for your app: the data is shared, resets periodically, and you don't control the schema. If you need persistent, private data with auth and logs, that's where an account-based backend or a commercial licence comes in.
What "free REST API for testing and prototyping" actually means
The phrase sounds vague, so it helps to separate two things people often conflate:
- A mock/sample API — a public, hosted service with fixed or semi-fixed endpoints that return realistic-looking JSON. You don't own the data. It exists so you can point code at a URL and get a response.
- A real backend you configure — a service where you define collections, schemas, authentication, and logging, and where your data persists and belongs to you.
ReqRes's landing page describes both: a free REST API for testing and prototyping with real responses and no signup, plus an option to build your own backend with collections, auth, and logs at app.reqres.in. Those are different products with different trade-offs. The free public endpoints are the "point and go" part; the account-based backend is the "own your data" part.
What you can do with the no-signup public endpoints
1. Front-end demos without a backend
If you're building a UI and need data to render, you can fetch from a public endpoint instead of hardcoding arrays. This keeps your demo code closer to real fetch logic:
async function loadUsers(page = 1) {
  const res = await fetch(`https://reqres.in/api/users?page=${page}`);
  if (!res.ok) throw new Error(`HTTP ${res.status}`);
  const { data, total, page: current } = await res.json();
  return { users: data, total, page: current };
}
You get pagination fields, a data array, and support metadata—enough to build list views, loading states, and empty states.
2. Integration and contract tests
You can assert that your HTTP layer handles status codes, headers, and JSON shapes correctly. Typical checks:
GET /api/users/2returns200with adataobject.GET /api/users/23returns404(a non-existent user).POST /api/loginwith valid credentials returns a token; with missing fields returns400.
This is useful for testing your client wrapper, retry logic, error handling, and serialization—without spinning up your own server.
3. Learning HTTP clients and tooling
If you're new to fetch, Axios, curl, Postman, or HTTPie, a hosted API is a low-friction target. You can practice:
- Sending query parameters (
?page=2,?delay=3). - Setting headers and reading response headers.
- Handling
POST,PUT,PATCH,DELETE. - Observing status codes for success and failure.
4. Deliberate failure and latency testing
Endpoints that return 404 on purpose, or that accept a delay parameter, let you test how your app behaves when things go wrong or slow down. That's hard to do reliably against a happy-path local mock.
What the public endpoints are not good for
| Use case | Public sample endpoints | Account-based backend |
|---|---|---|
| Persistent, private data | No — shared and reset | Yes |
| Custom schema/collections | No | Yes |
| Authentication you control | Limited (demo login) | Yes |
| Request logs and debugging | No | Yes |
| Production traffic | Not intended | Depends on plan/licence |
| Team collaboration | No | Yes |
The key limitation: you don't own the data, and other people are hitting the same endpoints. Treat responses as illustrative, not authoritative.
When you'd move to an account-based backend
Consider app.reqres.in (collections, auth, logs) when any of these are true:
- You need your own collections and fields, not the fixed demo schema.
- You need data to persist between sessions and belong only to you.
- You need real authentication flows you can rely on in a demo or internal tool.
- You need request logs to debug what your client actually sent.
- You're working with a team and need shared, stable endpoints.
The trade-off is setup and, eventually, cost. The public endpoints require none; the backend requires an account and configuration.
Where pricing and licensing become relevant
The site signals a commercial licence and an upgrade path (with Stripe as the payment platform), but specific prices, plan tiers, and limits aren't stated here—so don't assume numbers. What you can reason about:
- Prototyping and learning → free public endpoints are usually enough.
- Internal tools, demos for clients, or anything you don't want reset → an account-based backend is the natural next step.
- Production or commercial use → check the licence terms and any paid plan, because "free for testing" and "free for commercial production" are not the same thing.
Before committing, read the current terms on the site rather than relying on secondhand summaries, since pricing and licence scope change.
A quick decision checklist
- Do you need data that persists and is private? If yes → account-based backend.
- Do you need a custom schema? If yes → account-based backend.
- Are you only testing HTTP behavior, UI rendering, or learning a client? If yes → free public endpoints.
- Will this touch real users or revenue? If yes → review the licence and any paid plan first.
- Do you need logs and team access? If yes → account-based backend.
If you answer "no" to 1, 2, 4, and 5, the free hosted API is likely all you need. If you answer "yes" to any of them, plan for the account-based path.
Website Overview
An established domain and managed infrastructure suggest continuity of operations and may support dependable delivery, although neither guarantees service quality.
Domain and Registration
Registered in 2020, this domain has about 6 years of history. That suggests continuity, although ownership and purpose may have changed. Transfer-protection status is present, helping reduce the risk of unauthorized domain transfers. The registrar is NameCheap, Inc., a widely used domain service provider. Registration contact information is publicly available through RDAP. The domain uses the common .ai extension, which is not an independent safety signal.
DNS and Email
The lowest TTL is 28 seconds, supporting rapid record changes at the cost of more frequent lookups. Nameservers are provided by Amazon Route 53, indicating managed DNS hosting. MX records point to the Google Workspace email service. No CNAME was found; the observed records resolve directly to addresses. SPF and DMARC are configured. DKIM status is unknown.
TLS and Certificates
The certificate uses an RSA 2048-bit public key, offering broad client compatibility. The server supplied a complete certificate chain. No organization name is present in the certificate; the available fields are consistent with domain validation. The certificate was issued within the Amazon cloud or CDN ecosystem. The certificate is valid for about 393 days in total, with 175 days remaining.
HTTP and Browser Security
The response lacks these common security headers: CSP. No X-Powered-By header was found, reducing one common source of backend fingerprinting information. The cf-ray, x-cache, via response header indicates a CDN or caching proxy in the delivery path. No obvious internal addresses or debug information were found in the headers. The Server header identifies cloudflare without an exact version.
Technology Stack Analysis
The public page identifies Webflow, Cloudflare, Amazon CloudFront without precise versions, leaving fewer clues for version-specific scanning.
Search and Social Sharing
The meta description has 165 characters and may be shortened in search results. Twitter Card metadata is configured. The title has 58 characters, within a common display range. The observed directives allow indexing and link following. No Generator meta tag is publicly exposed.
 Hosting and Email
 Amazon Route 53
 Hosting

 Google Workspace
 Location
 United States
 Pages, Search and Sharing
| Meta description | Generate human-like speech and deploy Conversational agents with Murf AI. The complete AI Voice platform trusted by 10 million+ developers, businesses, and creators. |
|---|---|
| Canonical URL | https://murf.ai |
| Language | English (default) |
| Twitter Card | summary_large_image |
Social Sharing Preview
8 fieldsSharing metadata
| og:type | website |
|---|---|
| og:image | https://cdn.prod.website-files.com/66b3765153a8a0c399c70981/670584e2dab709883eed3793_Home.webp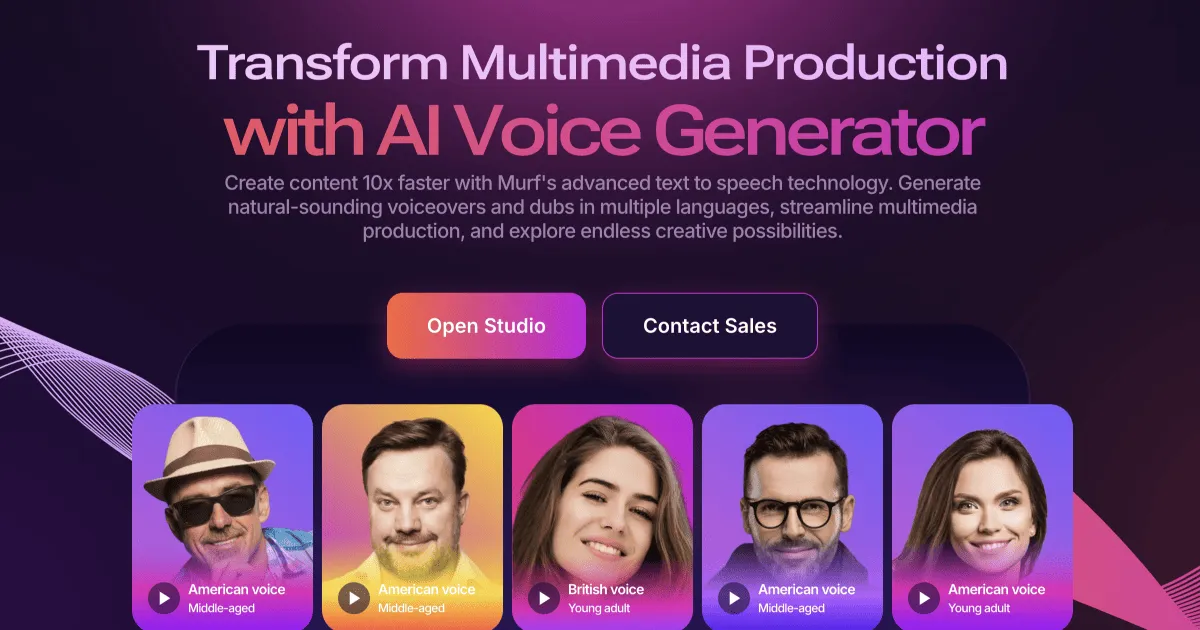 |
| og:title | Leading AI Voice & Conversational Agent Platform - Murf AI |
| og:description | Generate human-like speech and deploy Conversational agents with Murf AI. The complete AI Voice platform trusted by 10 million+ developers, businesses, and creators. |
| twitter:card | summary_large_image |
| twitter:image | https://cdn.prod.website-files.com/66b3765153a8a0c399c70981/670584e2dab709883eed3793_Home.webp |
| twitter:title | Leading AI Voice & Conversational Agent Platform - Murf AI |
| twitter:description | Generate human-like speech and deploy Conversational agents with Murf AI. The complete AI Voice platform trusted by 10 million+ developers, businesses, and creators. |
robots.txt (opens in a new tab)
5 rules
All bots 0 allowed · 5 disallowed

 All bots

/swagger.json/share//Share//Shared//shared/
No matching rules.
Sitemaps
3 Registration details RDAP / WHOIS
| Registrar | NameCheap, Inc. |
|---|---|
| Registered | 2020-07-17 |
| Expires | 2028-07-17 |
| Domain status | client transfer prohibited |
| Nameservers | ns-1117.awsdns-11.org、ns-1589.awsdns-06.co.uk、ns-288.awsdns-36.com、ns-739.awsdns-28.net |
| DNSSEC | unsigned |
 DNS records
| Type | Name | Value | TTL | Priority |
|---|---|---|---|---|
| A | murf.ai | 13.226.209.50 | 28 | — |
| A | murf.ai | 13.226.209.57 | 28 | — |
| A | murf.ai | 13.226.209.69 | 28 | — |
| A | murf.ai | 13.226.209.84 | 28 | — |
| MX | murf.ai | aspmx.l.google.com | 300 | 1 |
| MX | murf.ai | alt1.aspmx.l.google.com | 300 | 5 |
| MX | murf.ai | alt2.aspmx.l.google.com | 300 | 5 |
| MX | murf.ai | alt3.aspmx.l.google.com | 300 | 10 |
| MX | murf.ai | alt4.aspmx.l.google.com | 300 | 10 |
| NS | murf.ai | ns-1117.awsdns-11.org | 172800 | — |
| NS | murf.ai | ns-1589.awsdns-06.co.uk | 172800 | — |
| NS | murf.ai | ns-288.awsdns-36.com | 172800 | — |
| NS | murf.ai | ns-739.awsdns-28.net | 172800 | — |
| TXT | murf.ai | DirectFedAuthUrl=https://accounts.google.com/o/saml2/idp?idpid=C034ru7il | 300 | — |
| TXT | murf.ai | MS=ms34550255 | 300 | — |
| TXT | murf.ai | brevo-code:461432afddee653e5545546277dc8d90 | 300 | — |
| TXT | murf.ai | cursor-domain-verification-rg90h8=kSiH4lgIsT48UWeNFwAcTTuD3 | 300 | — |
| TXT | murf.ai | firebase=murf-283206 | 300 | — |
| TXT | murf.ai | google-site-verification=82Y3u030E-c_sybJr3qs18JXBaeRRk2gLRGZjVImtvc | 300 | — |
| TXT | murf.ai | google-site-verification=ZMNHzIWfVL3Y7WQW8r6APzBbDvrJ5SPFkxEOlk1TwEM | 300 | — |
| TXT | murf.ai | google-site-verification=mAe8O8HqAE9bz8sZV23Pvtc6uXhSrbmUk7ZUNhf2YxE | 300 | — |
| TXT | murf.ai | linkedin-site-verification=7484aa36-eacc-48cb-8f4a-5ee41bb4e143 | 300 | — |
| TXT | murf.ai | mixpanel-domain-verify=4e6f4116-4b2e-4bf6-ad0e-d59a178f65a9 | 300 | — |
| TXT | murf.ai | openai-domain-verification=dv-KWMxI1B9ZFvYj78I6vhAh5pd | 300 | — |
| TXT | murf.ai | rippling-domain-verification=e459ffc60367c16c | 300 | — |
| TXT | murf.ai | stripe-verification=5385A017AFC851D4A0F269ED9B163B9272296975D61983903E41EBC0B8F4E2F2 | 300 | — |
| TXT | murf.ai | v=spf1 include:_spf.firebasemail.com include:amazonses.com include:24360943.spf07.hubspotemail.net ~all | 300 | — |
| DMARC | _dmarc.murf.ai | v=DMARC1;p=quarantine;sp=none;pct=100;rua=mailto:[email protected];ruf=mailto:[email protected],mailto:[email protected];ri=86400;aspf=r;adkim=s;fo=1 | 300 | — |
 TLS and certificates
| Assessment | Normal configuration |
|---|---|
| Supported protocols | TLSv1.2、TLSv1.3 |
| Negotiated protocol | TLSv1.3 |
| Certificate subject | murf.ai |
| Issuer | Amazon |
| Valid until | 2027-03-15T23:59 · Remaining when checked: 175 days |
| Verification details | Certificate trust: Passed · Hostname match: Passed |
 HTTP response headers
| Header | Value |
|---|---|
| content-type | text/html; charset=utf-8 |
| cache-control | no-cache, no-store |
| server | cloudflare |
| strict-transport-security | max-age=31536000; includeSubDomains |
| x-frame-options | SAMEORIGIN |
| x-content-type-options | nosniff |
| referrer-policy | strict-origin-when-cross-origin |
| permissions-policy | camera=(), microphone=(self), geolocation=(self), payment=() |
 Identified technologies
Recent Updates
- Website images
- Screenshots
- Network details
- Website Technologies
- Pages and Search Information
- HTTP Response Information
- TLS and certificates
- DNS Information
- Domain Registration
- Website profile
- Website Description
- Website Name
- Website profile
- Website Description
- Website Name
User reviews (0)