
 it-tools.tech
No paid content found
Categories: Resources & Utilities
Collection of handy online tools for developers, with great UX. IT Tools is a free and open-source collection of handy online tools for developers & people working in IT.
 Visit website
 Updated: 2026-09-21 23:55
 Language: English (default)
 Access: Normal
 Profile views 1
 Outbound visits 0
Related questions
More questions →What Can You Actually Do With a Free Hosted REST API Like ReqRes?
A free hosted REST API like ReqRes gives you a real HTTP endpoint you can call immediately—no signup, no local server, no database setup. You get predictable JSON responses for users, resources, login, and registration, which makes it useful for front-end demos, integration tests, learning HTTP clients, and prototyping. What it is not is a production backend for your app: the data is shared, resets periodically, and you don't control the schema. If you need persistent, private data with auth and logs, that's where an account-based backend or a commercial licence comes in.
What "free REST API for testing and prototyping" actually means
The phrase sounds vague, so it helps to separate two things people often conflate:
- A mock/sample API — a public, hosted service with fixed or semi-fixed endpoints that return realistic-looking JSON. You don't own the data. It exists so you can point code at a URL and get a response.
- A real backend you configure — a service where you define collections, schemas, authentication, and logging, and where your data persists and belongs to you.
ReqRes's landing page describes both: a free REST API for testing and prototyping with real responses and no signup, plus an option to build your own backend with collections, auth, and logs at app.reqres.in. Those are different products with different trade-offs. The free public endpoints are the "point and go" part; the account-based backend is the "own your data" part.
What you can do with the no-signup public endpoints
1. Front-end demos without a backend
If you're building a UI and need data to render, you can fetch from a public endpoint instead of hardcoding arrays. This keeps your demo code closer to real fetch logic:
async function loadUsers(page = 1) {
  const res = await fetch(`https://reqres.in/api/users?page=${page}`);
  if (!res.ok) throw new Error(`HTTP ${res.status}`);
  const { data, total, page: current } = await res.json();
  return { users: data, total, page: current };
}
You get pagination fields, a data array, and support metadata—enough to build list views, loading states, and empty states.
2. Integration and contract tests
You can assert that your HTTP layer handles status codes, headers, and JSON shapes correctly. Typical checks:
GET /api/users/2returns200with adataobject.GET /api/users/23returns404(a non-existent user).POST /api/loginwith valid credentials returns a token; with missing fields returns400.
This is useful for testing your client wrapper, retry logic, error handling, and serialization—without spinning up your own server.
3. Learning HTTP clients and tooling
If you're new to fetch, Axios, curl, Postman, or HTTPie, a hosted API is a low-friction target. You can practice:
- Sending query parameters (
?page=2,?delay=3). - Setting headers and reading response headers.
- Handling
POST,PUT,PATCH,DELETE. - Observing status codes for success and failure.
4. Deliberate failure and latency testing
Endpoints that return 404 on purpose, or that accept a delay parameter, let you test how your app behaves when things go wrong or slow down. That's hard to do reliably against a happy-path local mock.
What the public endpoints are not good for
| Use case | Public sample endpoints | Account-based backend |
|---|---|---|
| Persistent, private data | No — shared and reset | Yes |
| Custom schema/collections | No | Yes |
| Authentication you control | Limited (demo login) | Yes |
| Request logs and debugging | No | Yes |
| Production traffic | Not intended | Depends on plan/licence |
| Team collaboration | No | Yes |
The key limitation: you don't own the data, and other people are hitting the same endpoints. Treat responses as illustrative, not authoritative.
When you'd move to an account-based backend
Consider app.reqres.in (collections, auth, logs) when any of these are true:
- You need your own collections and fields, not the fixed demo schema.
- You need data to persist between sessions and belong only to you.
- You need real authentication flows you can rely on in a demo or internal tool.
- You need request logs to debug what your client actually sent.
- You're working with a team and need shared, stable endpoints.
The trade-off is setup and, eventually, cost. The public endpoints require none; the backend requires an account and configuration.
Where pricing and licensing become relevant
The site signals a commercial licence and an upgrade path (with Stripe as the payment platform), but specific prices, plan tiers, and limits aren't stated here—so don't assume numbers. What you can reason about:
- Prototyping and learning → free public endpoints are usually enough.
- Internal tools, demos for clients, or anything you don't want reset → an account-based backend is the natural next step.
- Production or commercial use → check the licence terms and any paid plan, because "free for testing" and "free for commercial production" are not the same thing.
Before committing, read the current terms on the site rather than relying on secondhand summaries, since pricing and licence scope change.
A quick decision checklist
- Do you need data that persists and is private? If yes → account-based backend.
- Do you need a custom schema? If yes → account-based backend.
- Are you only testing HTTP behavior, UI rendering, or learning a client? If yes → free public endpoints.
- Will this touch real users or revenue? If yes → review the licence and any paid plan first.
- Do you need logs and team access? If yes → account-based backend.
If you answer "no" to 1, 2, 4, and 5, the free hosted API is likely all you need. If you answer "yes" to any of them, plan for the account-based path.
What Are Open-Source UI Element Libraries and How Do They Differ From UI Frameworks?
An open-source UI element library is a collection of individual, ready-made interface pieces—buttons, cards, inputs, toggles, loaders—that you copy into your own project and adapt. A UI framework, by contrast, is a structured system of components, conventions, and often a theming layer that governs how your whole interface is built. The practical difference: an element library gives you a snippet; a framework gives you a way of working. If you need a polished button in ten minutes, reach for the element library. If you're building a 40-screen product with a team, you probably want the framework.
What "open-source UI element library" actually means
The term gets used loosely, so it helps to separate the parts:
- Open-source: the code is publicly available, and the license tells you what you may do with it—copy, modify, redistribute, or use commercially.
- UI element: a single, self-contained piece of interface, usually small enough to read in one sitting. A button with hover states, a pricing card, a search field.
- Library: a browsable, searchable collection of those elements, typically contributed by many different people.
On a site like Uiverse, elements are shared by a community and written in plain CSS or Tailwind. You find one you like, copy the markup and styles, paste them into your project, and adjust colors, spacing, and text to fit. There's no package to install and no build step required—which is exactly the appeal, and also the source of most of the confusion.
Element library vs. UI framework: the core differences
| Dimension | Open-source UI element library | UI framework / design system |
|---|---|---|
| Unit of reuse | A single snippet you copy | A component you import or call |
| Installation | None; paste into your code | Package install, config, sometimes a provider |
| Consistency | Depends on you; each element may look different | Enforced by shared tokens and APIs |
| Theming | Manual edits per element | Central theme/config file |
| Updates | You own the copy; no upstream updates | Version bumps bring fixes and changes |
| Accessibility | Varies per contributor; must be checked | Usually tested and documented |
| Best for | Prototypes, landing pages, small sites, one-off needs | Multi-page apps, teams, long-lived products |
| Learning curve | Low—read the CSS | Higher—learn the API and conventions |
The table isn't a verdict. It's a map of trade-offs. Element libraries win on speed and freedom; frameworks win on consistency and maintenance.
Licensing and attribution: what to check before you paste
This is where people get into trouble, and it's worth slowing down for.
- Find the license. Every element or collection should state one. Common open-source licenses include MIT, Apache-2.0, and BSD. Some projects use copyleft licenses like GPL, which can impose obligations if you redistribute your code.
- Understand what the license permits. MIT and Apache-2.0 are permissive: you can typically use the code in commercial and closed-source projects. Copyleft licenses may require you to release derivative source under the same terms.
- Check attribution requirements. Permissive licenses usually require you to keep the copyright notice and license text somewhere in your project. That's a real obligation, not a formality.
- Look for per-element terms. On community sites, the site's overall terms and the individual contributor's stated wishes may differ. If a contributor asks for credit, honor it.
- When in doubt, ask or avoid. If a snippet has no license at all, you don't have clear permission to reuse it. Treat "no license" as "not open source," even if the code is publicly visible.
This article is general information, not legal advice. For commercial products with real exposure, have someone qualified review the licenses you're relying on.
How to use a community element in your project: a practical workflow
Here's a repeatable process that avoids most of the usual mess.
1. Start from a real need, not a browsing session
Decide what you need first—"a compact primary button with a loading state"—then search. Browsing aimlessly produces a pile of pretty snippets that don't fit together.
2. Copy the smallest version that works
Take the markup and the styles. Strip anything you don't need: demo wrappers, extra animations, decorative layers. Less code means fewer surprises.
3. Convert it to your conventions
If your project uses design tokens or CSS variables, replace hard-coded values:
/* Before: hard-coded */
.button { background: #4f46e5; border-radius: 8px; }

/* After: token-based */
.button { background: var(--color-primary); border-radius: var(--radius-md); }
This one step is what keeps a copied element from looking like a foreign object in your UI.
4. Check accessibility before you ship
Community elements vary widely here. Verify at minimum:
- Keyboard focus is visible and the element is reachable by Tab.
- Color contrast meets WCAG AA (4.5:1 for normal text).
- Interactive elements use semantic HTML (
<button>, not a clickable<div>). - Form inputs have associated labels.
- Motion respects
prefers-reduced-motion.
5. Test in context
Paste it into a real page with real content. Long labels, small screens, and dark mode break more copied elements than anything else.
6. Note where it came from
Keep a short comment or an internal credits file: source, license, date. Future you—and your legal reviewer—will be grateful.
Where element libraries genuinely shine
- Prototypes and demos: you need something clickable today, not a design system.
- Landing pages and marketing sites: a handful of distinctive elements, each custom.
- Filling gaps: your framework lacks one specific component, and you don't want to build it from scratch.
- Learning: reading well-made CSS is one of the fastest ways to improve.
- Small projects: a personal site doesn't need a theming architecture.
Where they fall short
- Consistency at scale: ten elements from ten contributors rarely look like one product.
- Maintenance: you own every copy. When your design changes, you edit each one.
- Accessibility debt: you inherit whatever the contributor did or didn't do.
- No upstream fixes: a bug fixed in the original won't reach your copy.
- Integration friction: different naming conventions, different units, different assumptions about resets.
When to choose which
Choose an element library when the scope is small, the timeline is short, or you need a few distinctive pieces rather than a whole system.
Choose a framework or design system when multiple people build multiple screens over months, when consistency is a product requirement, or when accessibility and theming need to be guaranteed rather than checked.
A hybrid works well for many teams: adopt a framework for the structural components—forms, navigation, layout—and borrow individual elements for the places where you want personality. Just route every borrowed element through the same token and accessibility checks, so it lands as part of your system rather than beside it.
The short version: open-source UI element libraries are a fast, flexible way to get good-looking interface pieces into a project. They are not a substitute for a design system, and the license and accessibility details are the part worth reading carefully.
Website Overview
An established domain and managed infrastructure suggest continuity of operations and may support dependable delivery, although neither guarantees service quality. An active inbound-mail setup with incomplete authentication may leave the domain more open to impersonation. Provider hosting alone does not close that gap.
Domain and Registration
Registered in 2020, this domain has about 6 years of history. That suggests continuity, although ownership and purpose may have changed. Transfer-protection status is present, helping reduce the risk of unauthorized domain transfers. The registrar is Squarespace Domains II LLC, a widely used domain service provider. The domain uses the common .tech extension, which is not an independent safety signal.
DNS and Email
The observed email authentication setup is incomplete: DMARC is missing. Nameservers are provided by Cloudflare, indicating managed DNS hosting. MX records point to the Mailgun email service. No CNAME was found; the observed records resolve directly to addresses. TXT records include verification markers for Google. Such markers may also remain after a service stops being used.
TLS and Certificates
The public key uses EC with 256 bits. The server supplied a complete certificate chain. No organization name is present in the certificate; the available fields are consistent with domain validation. The certificate was issued within the Google Trust Services cloud or CDN ecosystem. The certificate's total validity is about 90 days, consistent with a short renewal cycle.
HTTP and Browser Security
The response lacks these common security headers: HSTS, CSP, Permissions-Policy, clickjacking protection. CORS permits any origin to read this response. This is common for public resources; sensitive responses need narrower handling. No X-Powered-By header was found, reducing one common source of backend fingerprinting information. The cf-ray response header indicates a CDN or caching proxy in the delivery path. No obvious internal addresses or debug information were found in the headers.
Technology Stack Analysis
The public page identifies Cloudflare without precise versions, leaving fewer clues for version-specific scanning.
Search and Social Sharing
The meta description has 170 characters and may be shortened in search results. Twitter Card metadata is configured. The title has 44 characters, within a common display range. The observed directives allow indexing and link following. No Generator meta tag is publicly exposed.
 Hosting and Email
 Cloudflare
 Hosting

 Mailgun
 Location
 unknown
104.21.91.121
 Pages, Search and Sharing
| Meta description | Collection of handy online tools for developers, with great UX. IT Tools is a free and open-source collection of handy online tools for developers & people working in IT. |
|---|---|
| Canonical URL | https://it-tools.tech |
| Language | English (default) |
| Twitter Card | summary_large_image |
Social Sharing Preview
12 fields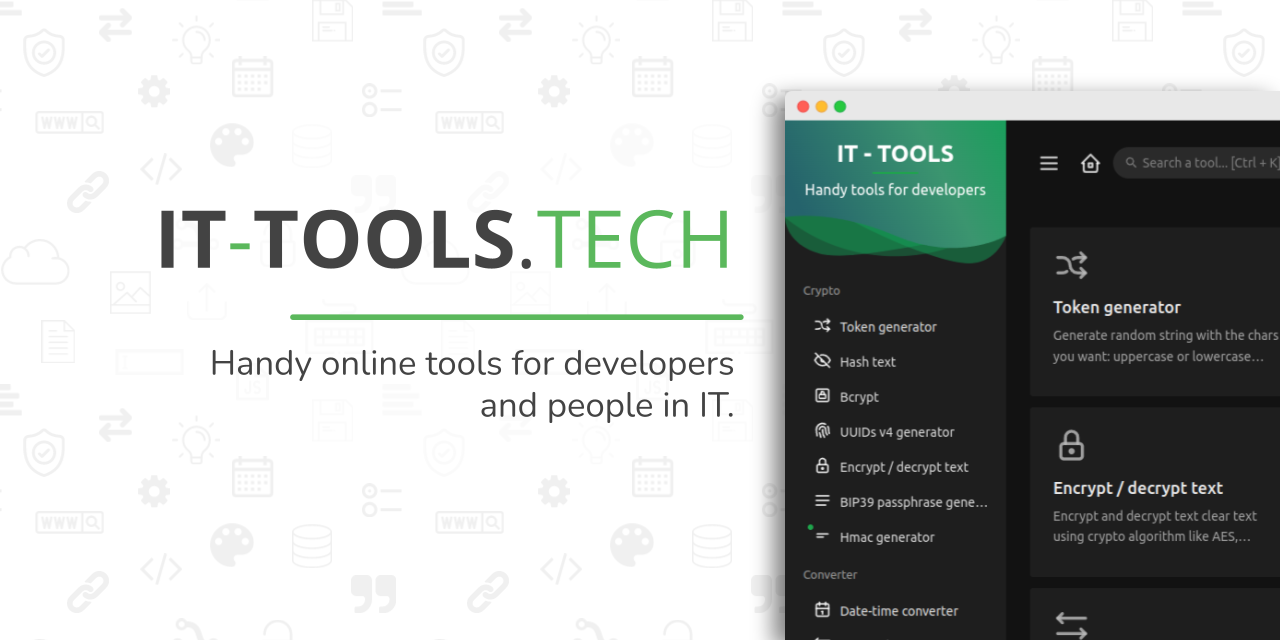

Sharing metadata
| og:url | https://it-tools.tech/ |
|---|---|
| og:type | website |
| og:image | https://it-tools.tech/banner.png?v=2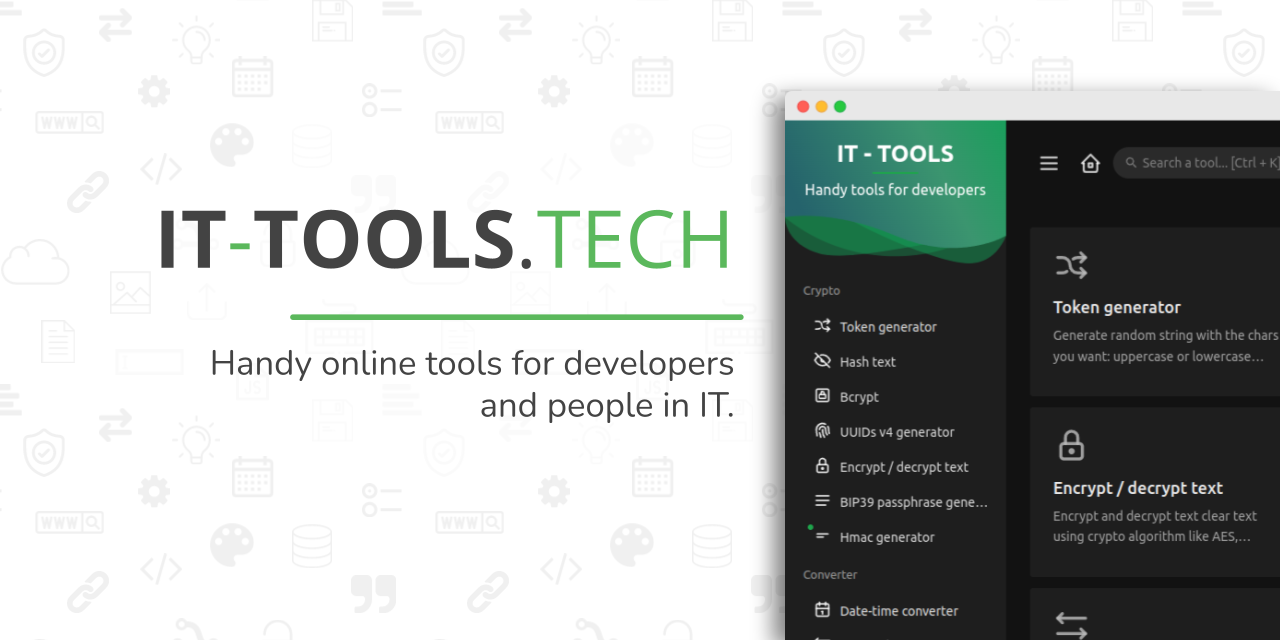 |
| og:title | IT Tools - Handy online tools for developers |
| og:description | Collection of handy online tools for developers, with great UX. IT Tools is a free and open-source collection of handy online tools for developers & people working in IT. |
| twitter:card | summary_large_image |
| twitter:site | @ittoolsdottech |
| twitter:image | https://it-tools.tech/banner.png?v=2 |
| twitter:title | IT Tools - Handy online tools for developers |
| twitter:creator | @cthmsst |
| twitter:image:alt | IT Tools - Handy online tools for developers |
| twitter:description | Collection of handy online tools for developers, with great UX. IT Tools is a free and open-source collection of handy online tools for developers & people working in IT. |
robots.txt (opens in a new tab)
0 rulesAll bots 0 allowed · 0 disallowed

 All bots
No matching rules.
Sitemaps
0No sitemaps found
 Registration details RDAP / WHOIS
| Registrar | Squarespace Domains II LLC |
|---|---|
| Registered | 2020-04-05 |
| Expires | 2027-04-05 |
| Domain status | client delete prohibited、client transfer prohibited |
| Nameservers | marge.ns.cloudflare.com、newt.ns.cloudflare.com |
| DNSSEC | unsigned |
 DNS records
| Type | Name | Value | TTL | Priority |
|---|---|---|---|---|
| A | it-tools.tech | 104.21.91.121 | 300 | — |
| A | it-tools.tech | 172.67.218.52 | 300 | — |
| AAAA | it-tools.tech | 2606:4700:3031::ac43:da34 | 300 | — |
| AAAA | it-tools.tech | 2606:4700:3032::6815:5b79 | 300 | — |
| MX | it-tools.tech | mxa.mailgun.org | 300 | 10 |
| MX | it-tools.tech | mxb.mailgun.org | 300 | 10 |
| NS | it-tools.tech | marge.ns.cloudflare.com | 86400 | — |
| NS | it-tools.tech | newt.ns.cloudflare.com | 86400 | — |
| TXT | it-tools.tech | google-site-verification=tgyUvmbCXc5wSh_7iASYaHrbLzmqvk23DSpHk5O2l2g | 300 | — |
| TXT | it-tools.tech | v=spf1 include:mailgun.org ~all | 300 | — |
 TLS and certificates
| Assessment | Normal configuration |
|---|---|
| Supported protocols | TLSv1.2、TLSv1.3 |
| Negotiated protocol | TLSv1.3 |
| Certificate subject | it-tools.tech |
| Issuer | Google Trust Services |
| Valid until | 2026-11-28T05:58 · Remaining when checked: 67 days |
| Verification details | Certificate trust: Passed · Hostname match: Passed |
 HTTP response headers
| Header | Value |
|---|---|
| content-type | text/html; charset=utf-8 |
| cache-control | public, max-age=0, must-revalidate |
| server | cloudflare |
| x-content-type-options | nosniff |
| referrer-policy | strict-origin-when-cross-origin |
| access-control-allow-origin | * |
 Identified technologies
Recent Updates
- Website images
- Screenshots
- Network details
- Website Technologies
- Pages and Search Information
- HTTP Response Information
- TLS and certificates
- DNS Information
- Domain Registration
- Website profile
- Website Description
- Website Name
- Website profile
- Website Description
- Website Name
User reviews (0)